📅24 November 2026 | 9:30 – 17:00 EET | Sofia Tech Park, Sofia, Bulgaria| Hybrid | English
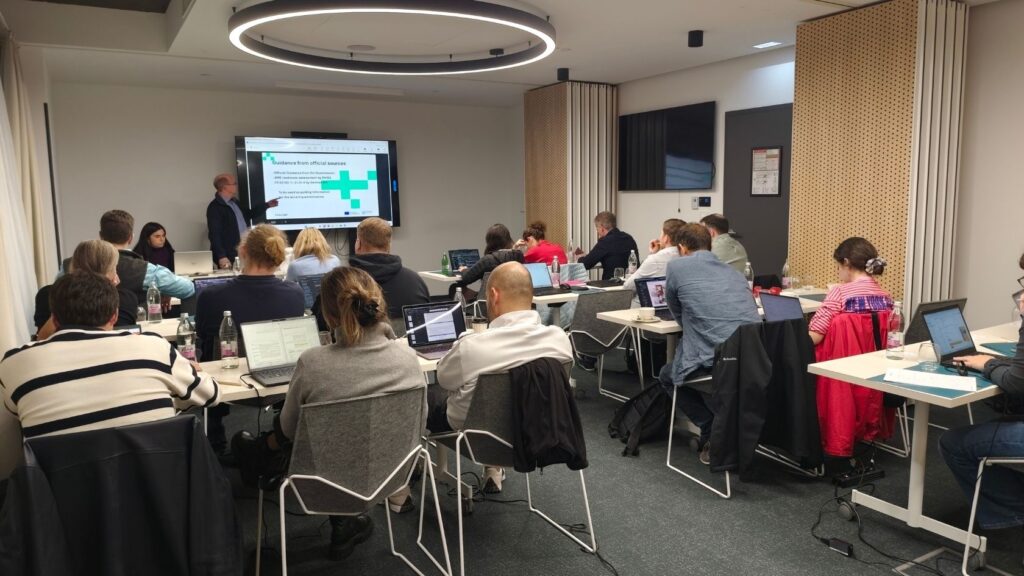
On 24 November, CRACoWi will join CRA Standards Unlocked – EU Tour at Sofia Tech Park, Bulgaria, bringing together cybersecurity experts, standardisation specialists, EU-funded projects and companies preparing for the Cyber Resilience Act (CRA).
As organisations move towards CRA compliance, understanding the requirements is only the beginning. The real challenge is putting them into practice, identifying relevant standards and finding tools that can support the process.
Katherine Leese from our consortium partner SevenShift will represent CRACoWi and introduce Bunkai, a tool developed within the CRACoWi project to support practical CRA compliance.
The event is also an opportunity to learn more about the ongoing development of harmonised CRA standards, discover solutions from other European projects and exchange knowledge with organisations working on similar challenges.
Are you developing or manufacturing digital products, preparing for CRA compliance, or interested in collaborating with CRACoWi? Join us to discover our work, ask questions and explore opportunities for cooperation.
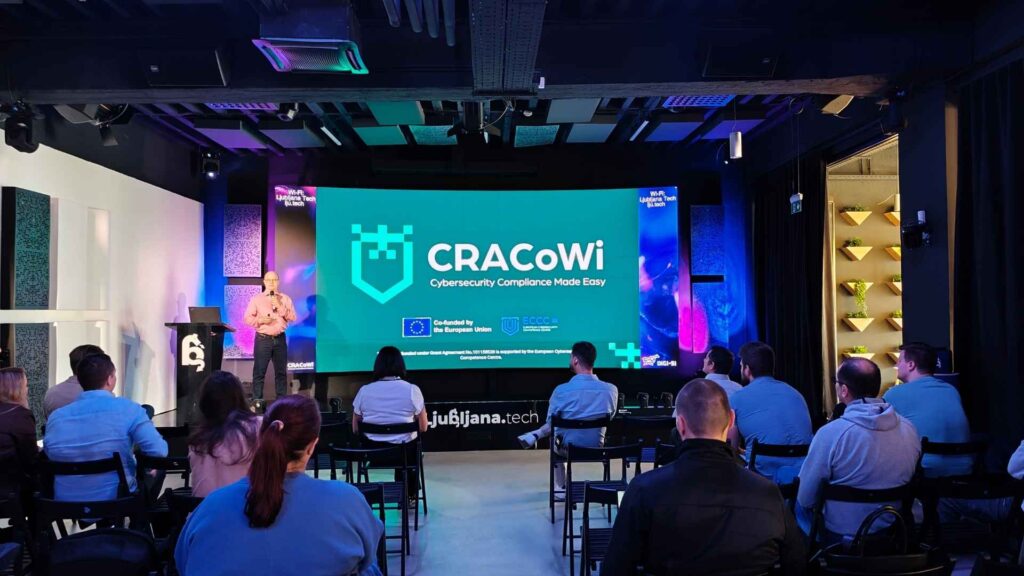
The CRACoWiconsortium gathered in Ljubljana, Slovenia, on 14 October 2026 for its fourth plenary meeting, hosted by project partner Digital Innovation Hub Slovenia (DIH Slovenia). The meeting brought together consortium partners to review project progress, discuss the development and validation of the CRACoWi Wizard, and align priorities for the final year of the project.
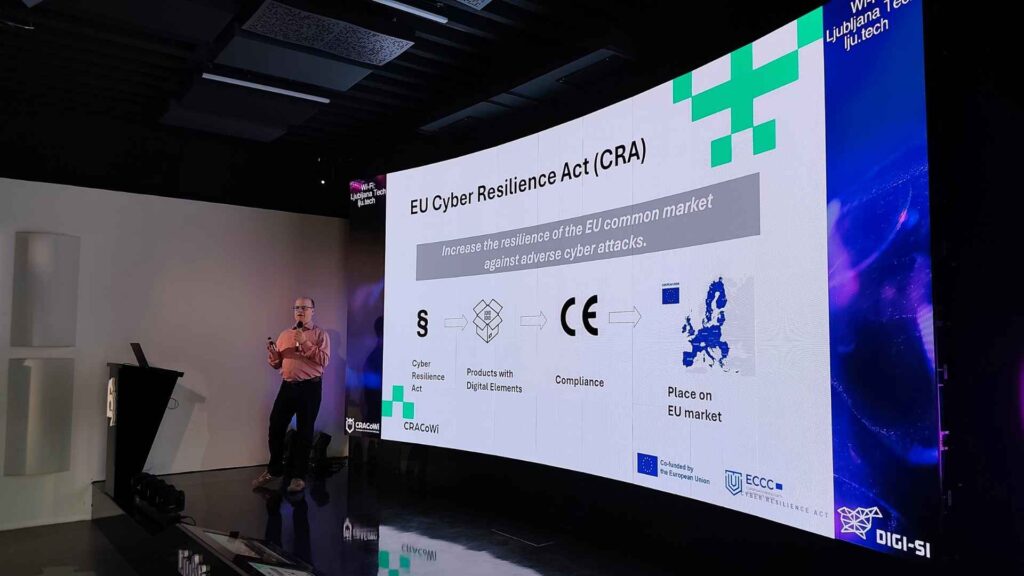
The two-day gathering continued on 15 October with the consortium’s participation in Cyber Day 2026, providing an opportunity to engage with companies, cybersecurity experts and European initiatives working to strengthen cyber resilience and support the implementation of the Cyber Resilience Act (CRA).
Advancing the CRACoWi Wizard Towards Validation
With the project entering its final year, the Ljubljana plenary focused on moving from development towards implementation, validation and the practical application of project results.
A technical workshop brought partners together to review the current status of the CRACoWi Wizard’s functionalities, demonstrate the user journey and discuss the next steps in its development. Particular attention was given to the implementation and validation roadmap, including cooperation with use case owners and preparations for validating the Wizard against practical CRA compliance scenarios.
These activities are essential to ensuring that the Wizard responds to the needs of companies navigating the Cyber Resilience Act, particularly SMEs, manufacturers, distributors and importers.
Aligning Technical Development with CRA Requirements
As the European regulatory and standardisation landscape continues to evolve, the consortium also addressed developments in CRA standardisation and certification. Michael Beine from Bureau Veritas contributed an update on the status and roadmap of relevant standards and certification activities, including their implications for the CRACoWi Wizard.
The meeting also covered preparations for the final phase of project activities related to evidence and traceability, shared knowledge, feedback and coordination with use case partners. Alongside technical development, partners reviewed communication, dissemination and capacity-building activities, including project KPIs and priorities for the final year.
These discussions supported a shared understanding of the work ahead and the importance of connecting technical results with practical support for stakeholders.
Connecting with Companies at Cyber Day 2026
The consortium gathering continued on 15 October with participation in Cyber Day 2026, an event focused on translating cybersecurity requirements into practical action.
As an event partner (organiser), CRACoWi contributed to the programme through its expertise on the Cyber Resilience Act and the tools being developed to support companies preparing for compliance.
Michael Beine from Bureau Veritas addressed the CRA from the SME perspective, while Pablo Endres from Seven Shift and Jacek Trossen from ONEKEY presented CRACoWi tools, giving participants an opportunity to learn more about the project’s approach to supporting CRA compliance.
Cyber Day also brought together representatives of other European cybersecurity initiatives like INTERCEPT and ALiEnS-SOC projects, creating opportunities for knowledge exchange, stakeholder engagement and collaboration.
For CRACoWi, participation provided a valuable opportunity to connect project development with the challenges faced by companies and to introduce the support available through the project.
Looking Ahead to the Final Year
The Ljubljana plenary marked an important point in CRACoWi’s implementation, with the consortium concentrating on the activities needed to bring its results closer to practical use.
Over the coming months, attention will remain on advancing the Wizard, working with use case partners on validation, incorporating relevant regulatory and standardisation developments, and expanding stakeholder engagement and capacity-building activities.
Through the CRACoWi Wizard, free CRA Scope Assessment and CRAcademy resources, the project aims to make CRA compliance more accessible and manageable, particularly for SMEs.
The consortium thanks Digital Innovation Hub Slovenia for hosting the fourth plenary meeting and all partners for their continued contributions. The two days in Ljubljana provided an opportunity to strengthen coordination within the consortium while connecting the project’s work with the wider European cybersecurity community.
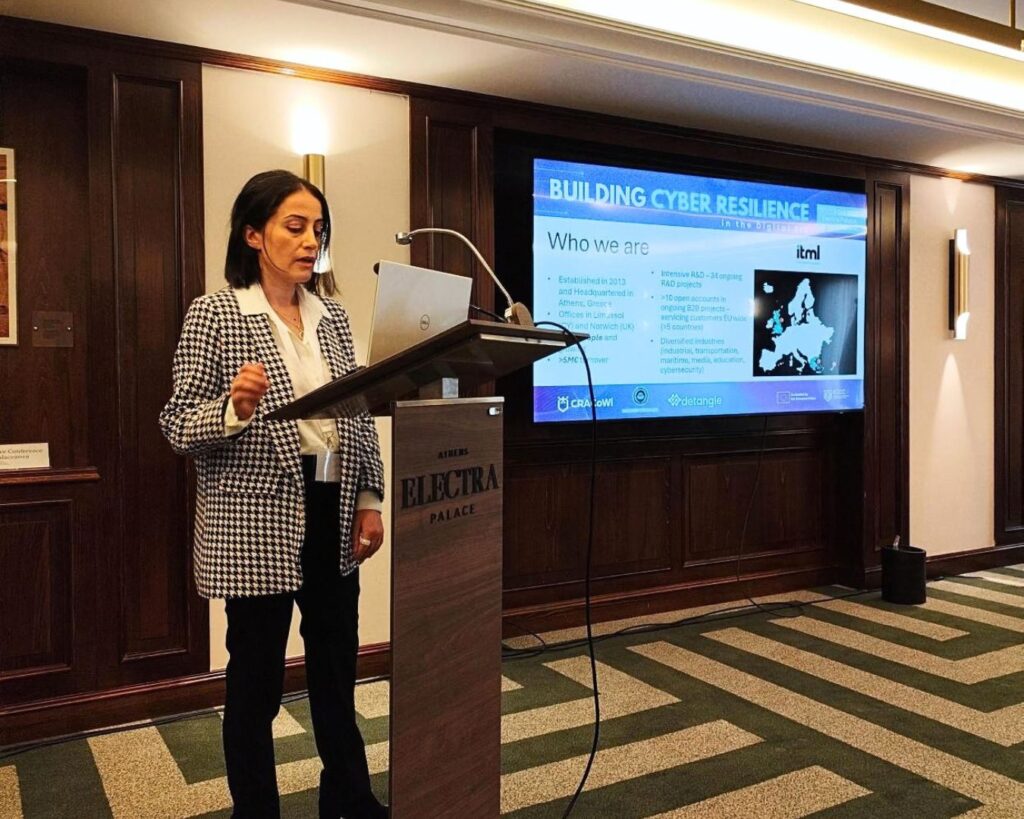
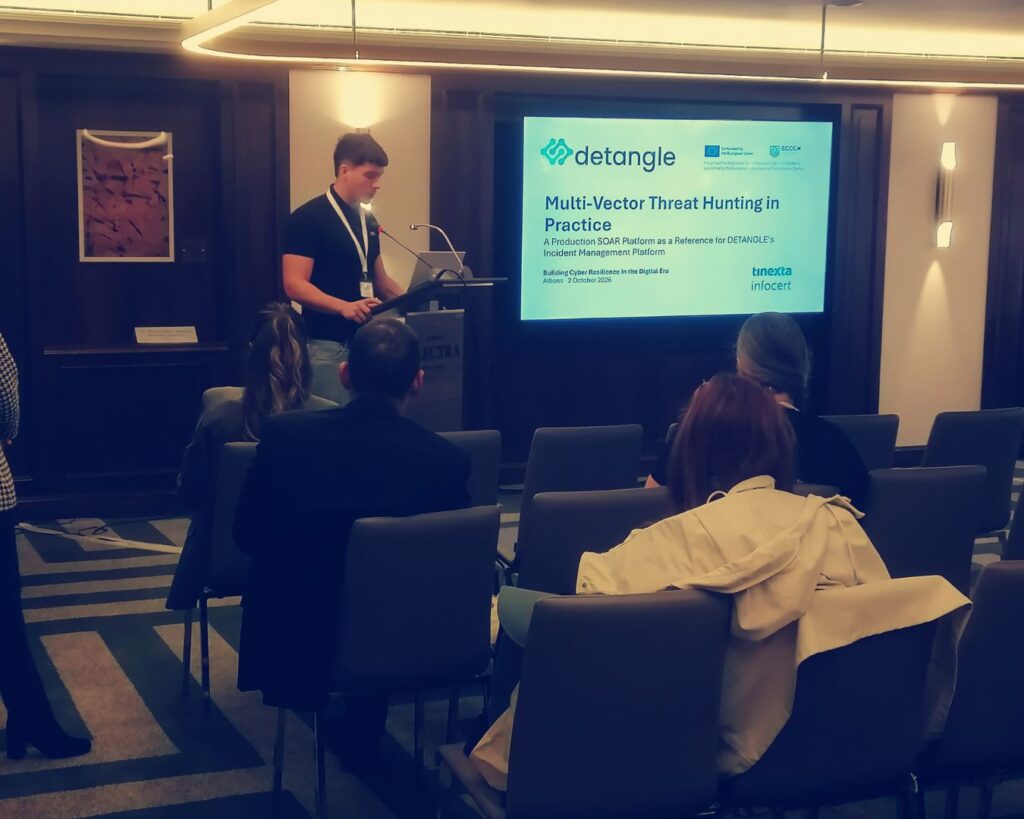
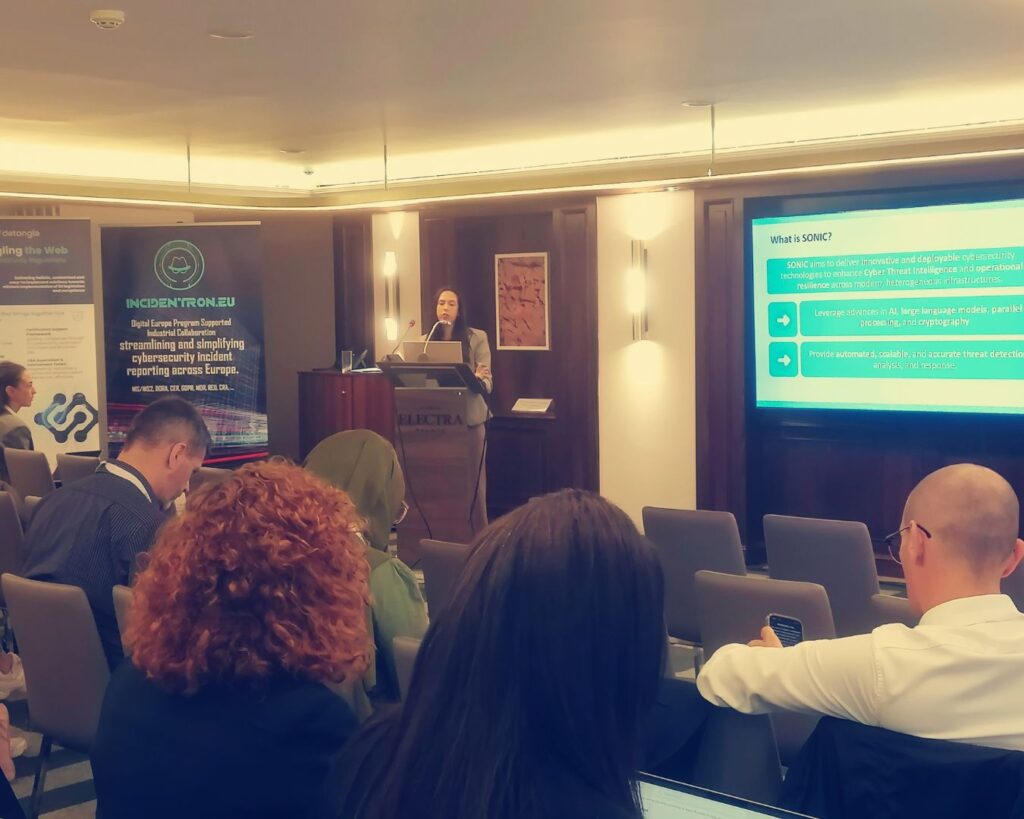
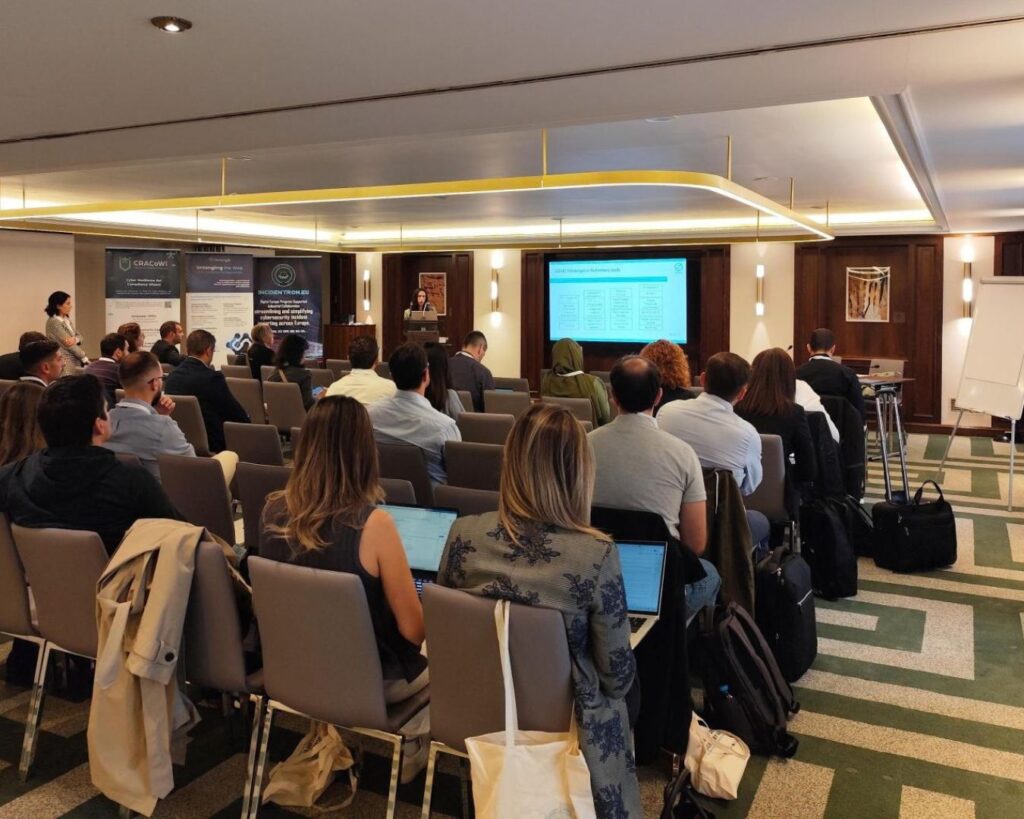
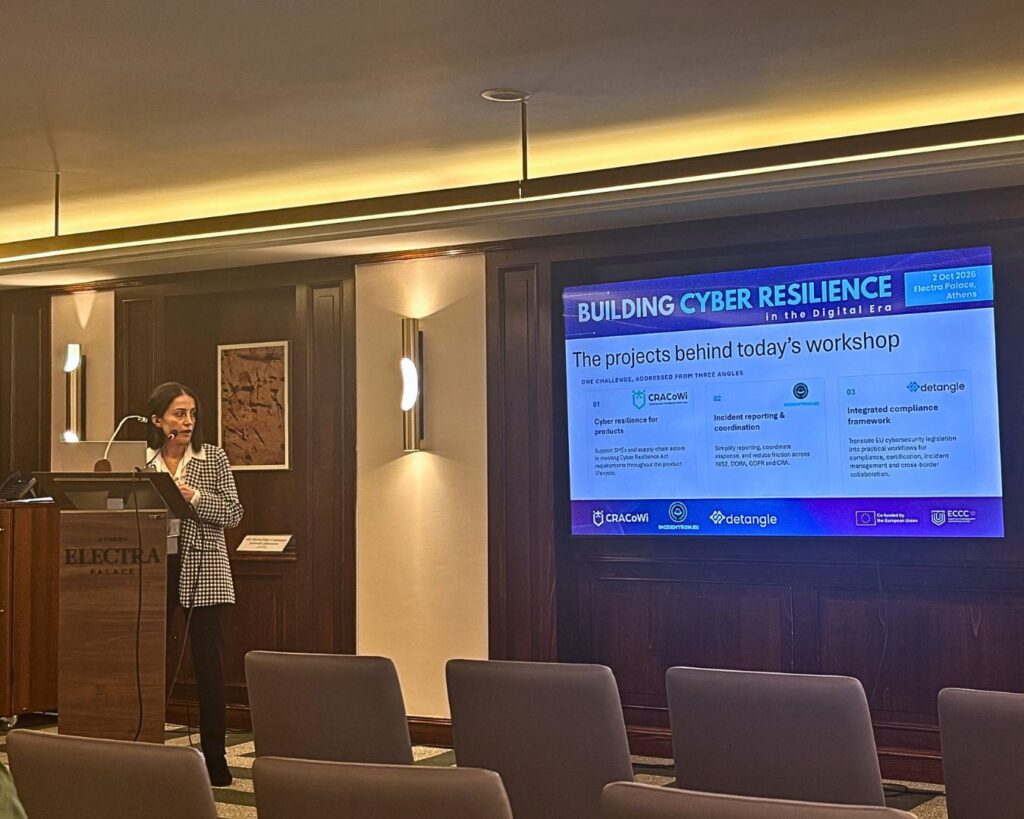
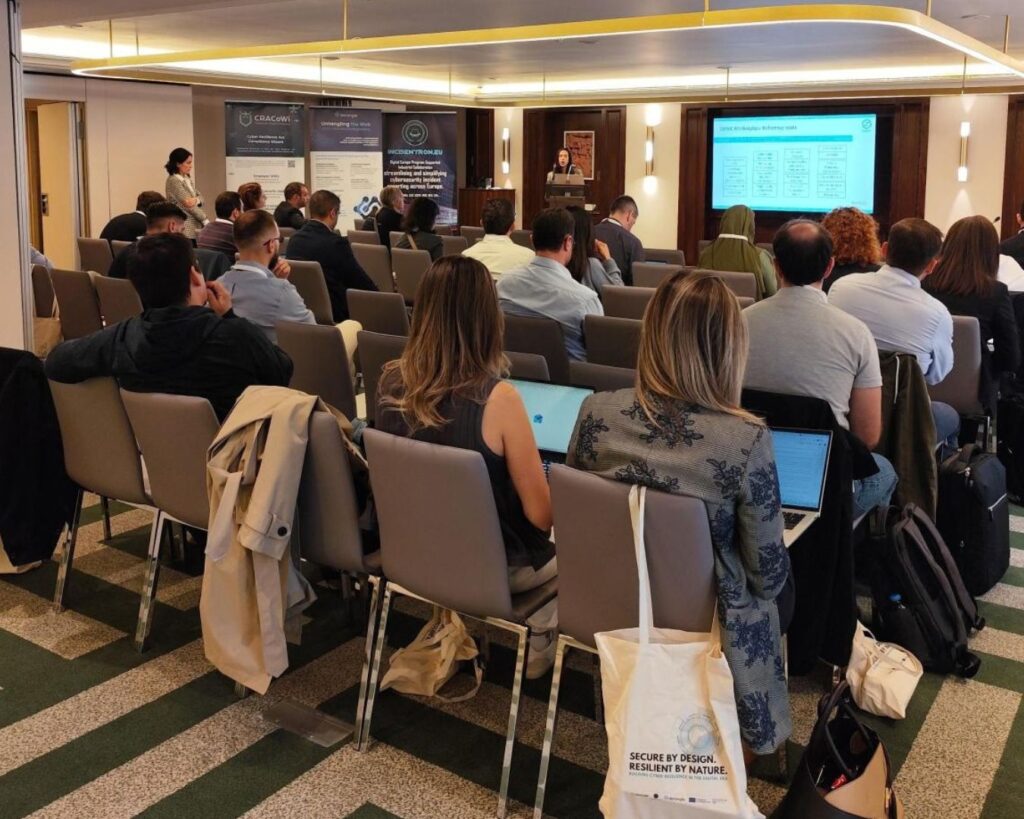
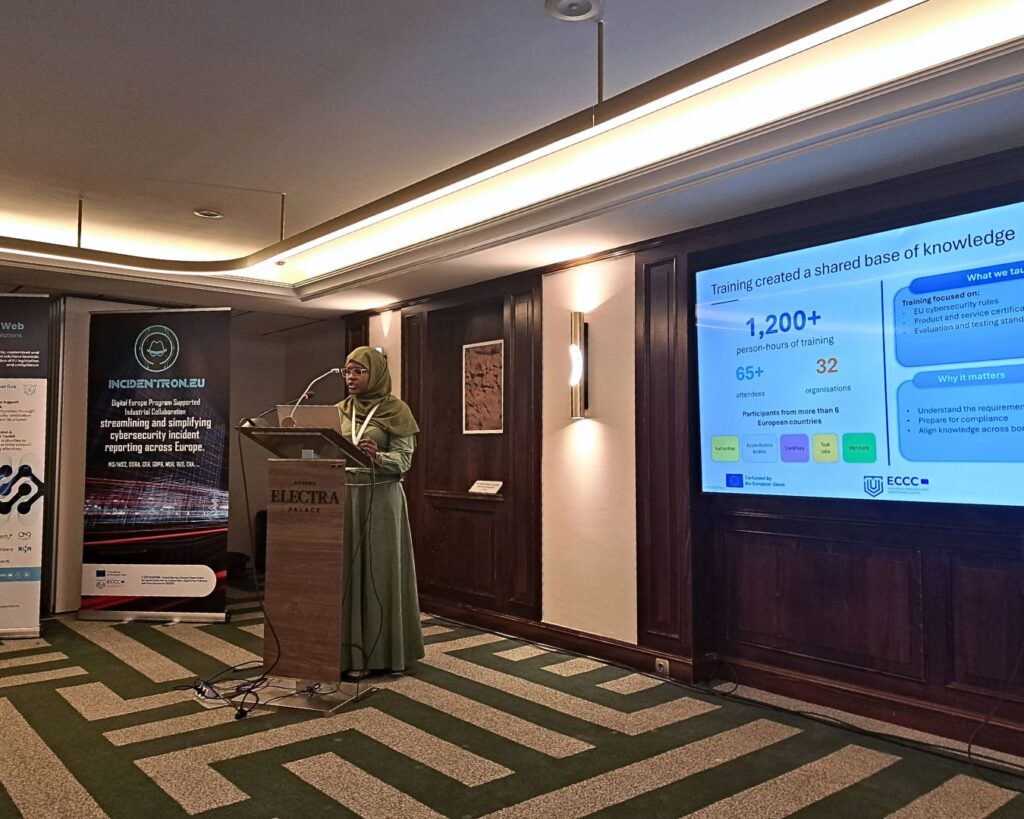
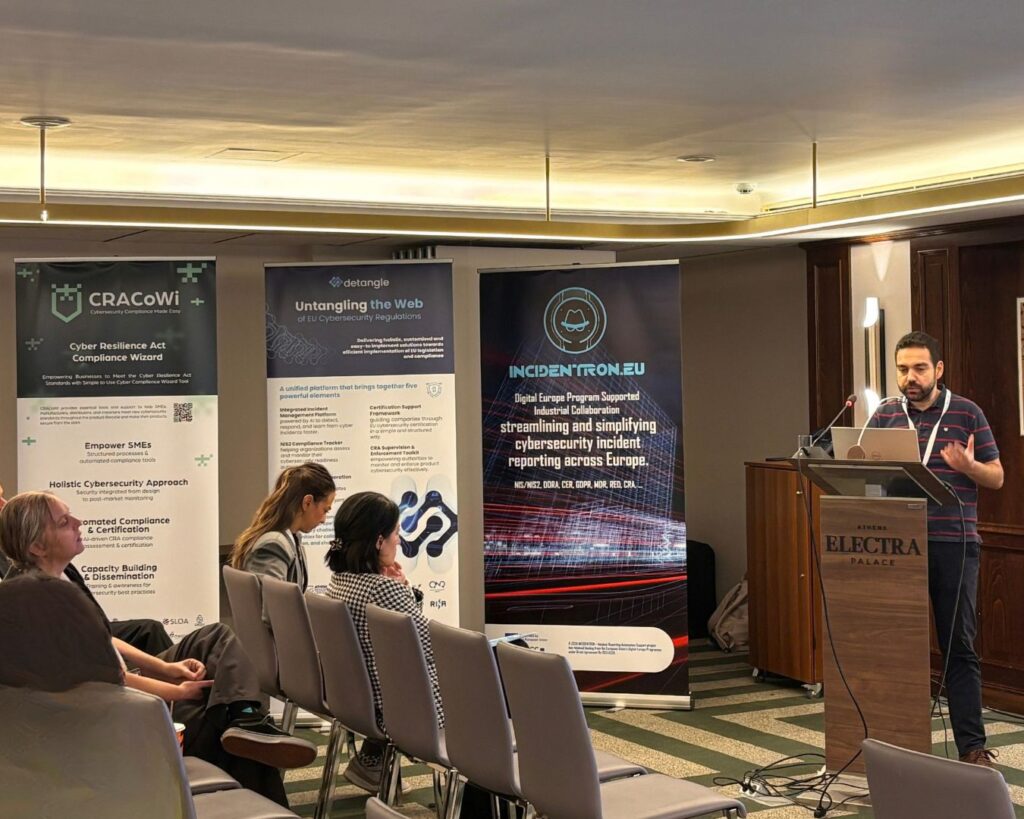
How can European cybersecurity projects and collaboration between them help turn regulatory requirements into practical action? This was one of the central question at Building Cyber Resilience in the Digital Era, held on 2 October 2026 in Athens, Greece.
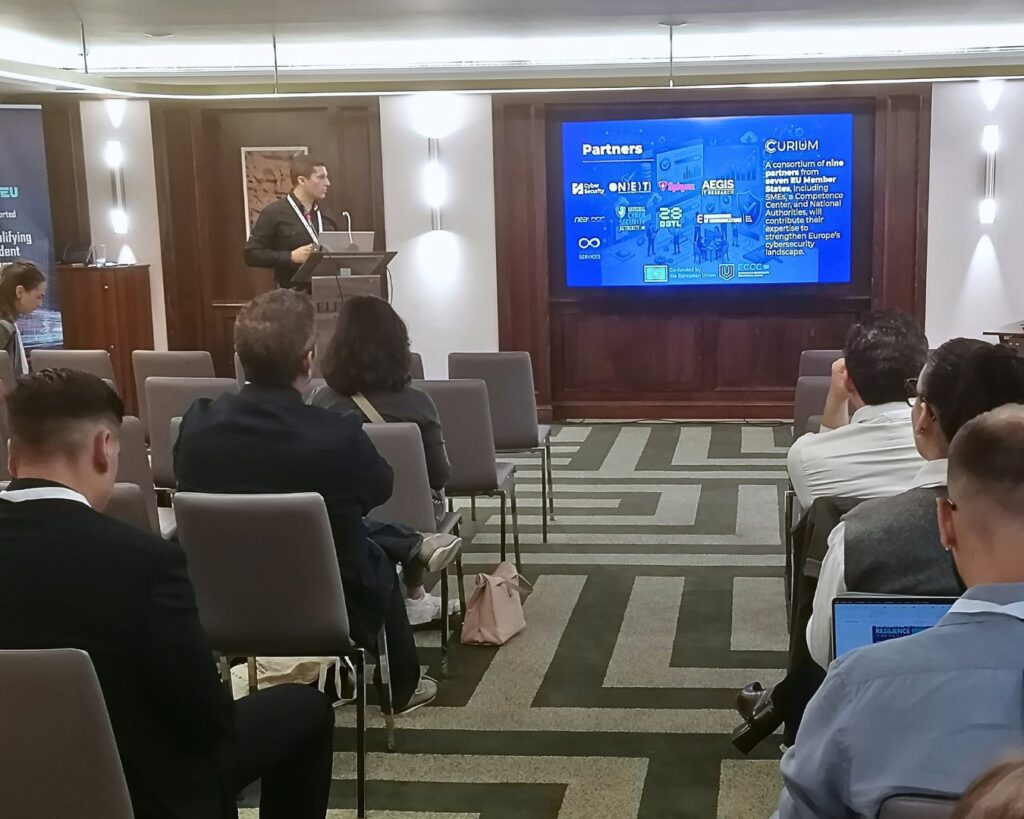
Jointly organised by the EU-funded projects CRACoWi, DETANGLE and INCIDENTRON, the event brought together more than 40 participants and representatives of 11 EU-funded projects to exchange knowledge, share experiences and explore opportunities for collaboration in strengthening Europe’s cybersecurity resilience.
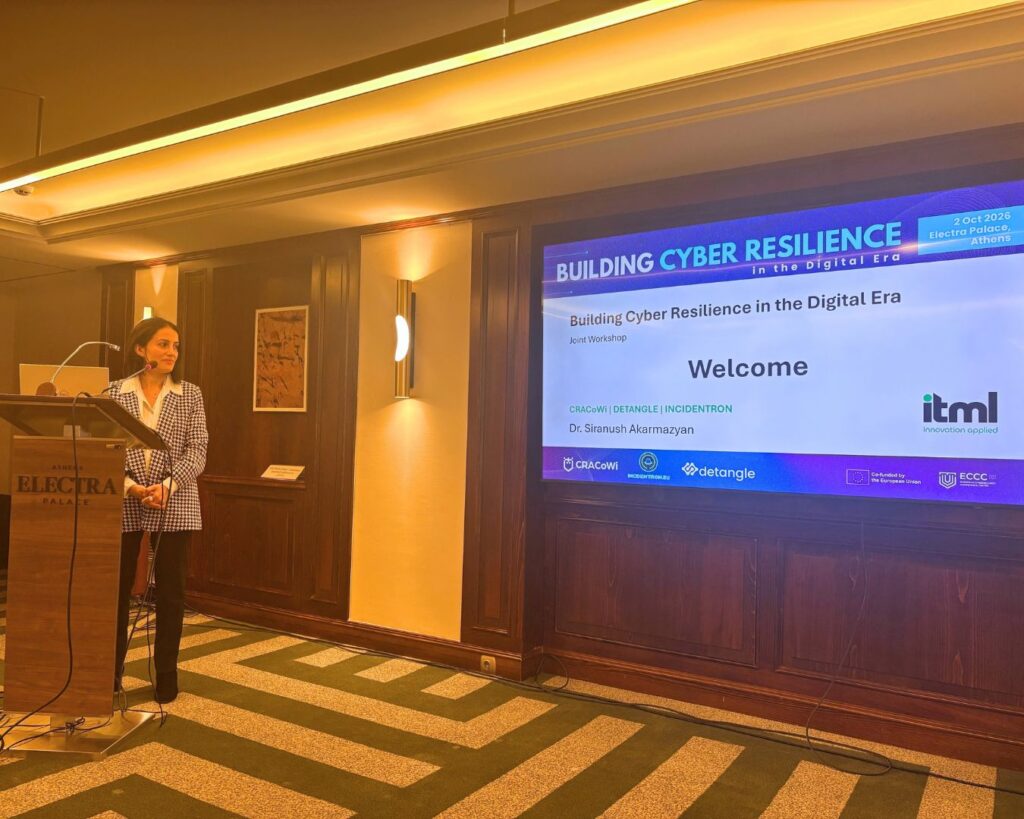
The event was opened by Dr. Siranush Akarmazyan (ITML), setting the stage for discussions on the challenges and opportunities surrounding cybersecurity regulation and its practical implementation.
The event focused on three closely connected areas: the NIS2 Directive, the Cyber Resilience Act (CRA), and cross-border cybersecurity incident response.
These topics represent different but complementary aspects of Europe’s approach to cybersecurity. While regulatory frameworks establish requirements and responsibilities, organisations also need practical knowledge, tools and capabilities to implement them effectively.
The workshop brought together representatives of CRACoWi, DETANGLE, INCIDENTRON, OSCRAT, SONIC, CURIUM, WEM Cyber, CYBERFORT, CyberSynchrony, APPtake and TrustBoost.
Each project contributes to the broader European cybersecurity ecosystem, and bringing them together provided an opportunity to exchange experiences and identify common interests across their activities.
Moving Beyond Compliance
One of the central messages of the event was that building digital resilience requires more than compliance – it requires continuous collaboration, preparedness and action.
For CRACoWi, this message is particularly relevant. The project is developing practical support to help companies, especially SMEs, understand and address Cyber Resilience Act requirements through the CRACoWi Wizard, free CRA Scope Assessment and CRAcademy knowledge resources.
However, CRA implementation does not happen in isolation. Companies operate in a broader cybersecurity environment where regulatory obligations, technical challenges and operational preparedness are increasingly interconnected.
Events bringing together complementary EU-funded initiatives provide an opportunity to share expertise, learn from different approaches and strengthen the connections needed to support organisations effectively.
Strengthening Collaboration Between EU-Funded Projects
Beyond individual project activities, the workshop highlighted the value of cooperation within the European cybersecurity ecosystem.
Bringing together 11 projects around shared challenges created opportunities for knowledge exchange and further collaboration, helping participating initiatives better understand each other’s work and identify areas of common interest.
For CRACoWi, such exchanges are an important part of connecting the project’s activities with the wider European efforts to strengthen cybersecurity and support organisations facing new regulatory requirements.
The event reflected a shared ambition among the participating projects: to turn regulation into action, compliance into resilience, and shared challenges into opportunities for collaboration.
CRACoWi thanks the co-organisers, participating projects, speakers and all attendees who contributed to the event and its discussions.
We look forward to continuing the exchange and building on the connections established in Athens.
📅7 October 2026 | 9:00 – 17:00 CEST | CITYHUB, Am Hauptbahnhof 6, Bonn| Hybrid | English & Germany | Free
The CRACoWi team is heading to Bonn!
On 7 October 2026, CRACoWi will join fellow European projects, cybersecurity experts, standardisation specialists and companies at CRA Standards Unlocked – EU Tour in Bonn, part of a European workshop series dedicated to helping organisations understand and prepare for the Cyber Resilience Act (CRA).
CRACoWi partners Bureau Veritas, SevenShift, ONEKEY and Erminas will be there, and we invite companies, SMEs and other stakeholders working on CRA compliance to join us and meet the team.
From CRA Requirements to Standards and Practical Compliance
As companies move from understanding the Cyber Resilience Act towards its practical implementation, questions around standards are becoming increasingly important.
Which standards will support CRA compliance? How are harmonised standards being developed? What will they mean for product development and conformity assessment? And what practical tools are already available to help companies prepare?
CRA Standards Unlocked will bring these discussions together in one place.
The programme will cover the CRA standardisation process and the roles of European and national standardisation organisations, followed by presentations on horizontal and product-specific standards currently under development.
Participants will also hear about CRA market surveillance, implementation from a manufacturer’s perspective and how CRA compliance could influence the European digital single market and cybersecurity landscape.
Discover CRA Compliance Tools and Support
Understanding the standards is only one part of preparing for the CRA. Companies also need practical ways to translate regulatory requirements into their own processes and products.
Dedicated sessions at the event will therefore introduce compliance tools and funding opportunities being developed through Digital Europe Programme projects.
This is also where collaboration between projects working within the wider CRA ecosystem becomes particularly valuable. By bringing together different expertise, tools and approaches, CRA Cluster initiatives can help companies find the support that best responds to their specific compliance challenges.
CRACoWi is contributing to this effort by developing practical support for organisations navigating the CRA, including the CRACoWi Wizard, CRAcademy resources and the free CRA Scope Assessment.
Meet the CRACoWi Team in Bonn
For CRACoWi, events such as CRA Standards Unlocked are an important opportunity not only to share what we are developing, but also to meet companies directly, hear about their challenges and exchange knowledge with other projects working towards practical CRA implementation.
Representatives from Bureau Veritas, SevenShift, ONEKEY and OIXIO Erminas will represent CRACoWi in Bonn.
If you are preparing for the CRA, working with products with digital elements or simply want to understand how standards and practical compliance tools can support your organisation, come and meet the CRACoWi team.
📅 7 October 2026 | 09:00–17:00 📍 CITYHUB, Am Hauptbahnhof 6, 53111 Bonn, Germany 💻 Hybrid event – onsite and online participation
Onsite participation is limited, so make sure to register in advance.
Join us in Bonn and be part of the conversation on turning CRA requirements and standards into practical compliance.
📅15 October 2026 | 9:00 – 15:00 CEST | Ljubljana.tech, BTC Ljubljana | English | Free
How can companies move from understanding cybersecurity requirements to actually implementing them?
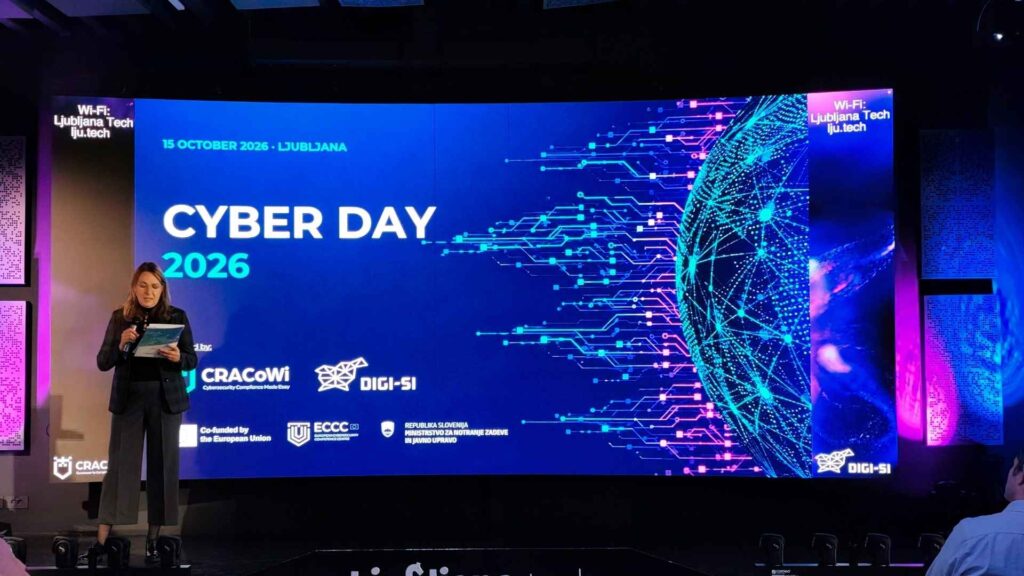
On 15 October 2026, CRACoWi will join cybersecurity experts, companies and European initiatives at Cyber Day 2026 in Ljubljana, an event dedicated to turning cybersecurity requirements into practical action and strengthening the cyber resilience of European companies.
As a partner of the event, CRACoWi will contribute its expertise on the Cyber Resilience Act (CRA) and present some of the practical support being developed to help companies navigate the path towards compliance.
Cyber Day will take place from 09:00 to 15:00 at Ljubljana.tech, Trg mladih 9, Ljubljana.
From CRA Requirements to Practical Action
The Cyber Resilience Act introduces new cybersecurity requirements for products with digital elements, creating new responsibilities for companies across the product lifecycle. For many SMEs, the challenge is not only understanding these requirements but also knowing how to approach them in practice. This will be one of the key topics addressed at Cyber Day.
Michael Beine from Bureau Veritas, CRACoWi partner and cybersecurity and regulatory compliance expert, will present “CRA Explained for SMEs”, looking at what the regulation means specifically for smaller companies.
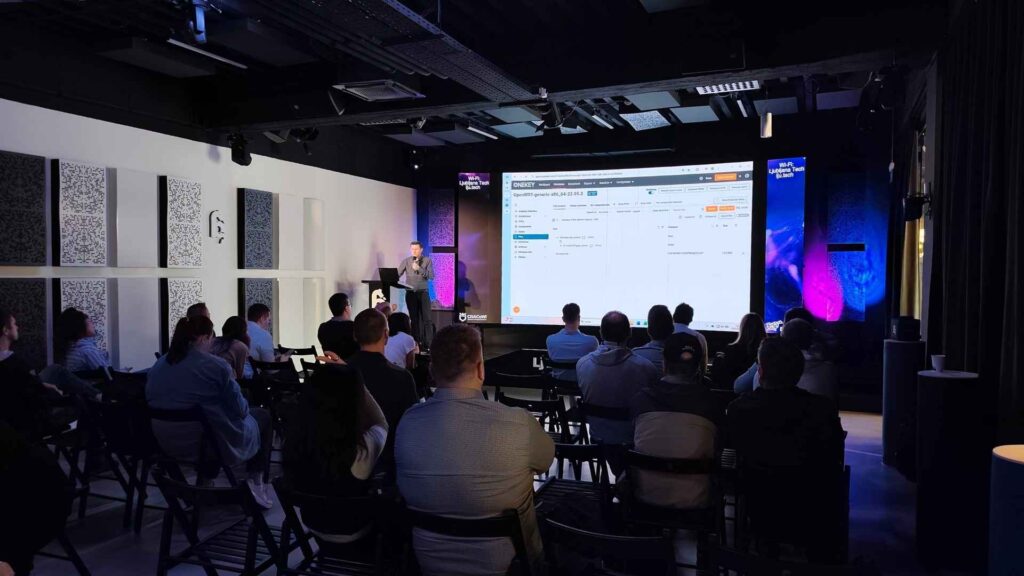
This will be followed by a CRACoWi tools demonstration by Jacek Trossen from ONEKEY, giving participants an opportunity to learn more about the practical support being developed within the project.
The programme will continue by moving from compliance to action, including a panel discussion dedicated to the question “How can SMEs become cyber resilient?”
Meet the Wider Cybersecurity Ecosystem
Cyber Day is not only about understanding regulation. It is also an opportunity to discover the organisations, projects, tools and funding opportunities available to companies working to strengthen their cybersecurity.
The programme will bring together representatives of the CRA Cluster and several Digital Europe projects, including CyberSynchrony, ALiEnS-SOC and INTERCEPT.
Participants will also hear about the wider cybersecurity support ecosystem and EU funding opportunities for cyber resilience.
Alongside the conference programme, the Cybervillage will provide space to meet experts, European projects and support organisations directly, exchange experiences and explore opportunities for further cooperation.
Who Should Join?
Cyber Day is designed particularly for micro, small and medium-sized enterprises looking to strengthen their cyber resilience and better understand the regulatory requirements affecting their businesses.
The event will be especially relevant for companies preparing for the Cyber Resilience Act, organisations looking for practical cybersecurity support, and stakeholders interested in the European cybersecurity ecosystem, available tools and EU funding opportunities.
Whether you are already working on CRA compliance or are only beginning to understand what the new requirements mean for your organisation, Cyber Day provides an opportunity to ask questions, meet experts and discover the support already available.
Meet CRACoWi in Ljubljana
For CRACoWi, Cyber Day is also an opportunity to meet companies directly, better understand the challenges they face and present the practical support the project is developing for CRA implementation.
If the Cyber Resilience Act is on your agenda, come and meet the CRACoWi team in Ljubljana. Talk to our experts, learn more about the project and discover how CRACoWi can support your journey towards CRA compliance.
15 October 2026 | 09:00–15:00 Ljubljana.tech, Trg mladih 9, Ljubljana
Participation is free of charge, but registration is required.
CRACoWi has been featured in a new article by Frank Bold, introducing the project and the support it offers to small and medium-sized enterprises preparing for the Cyber Resilience Act (CRA).
The article, published on 17 September, is part of a series aimed at helping Czech companies navigate CRA implementation by introducing European projects, resources and tools that can support them in this process. In the latest interview, Kristína Šabová from Frank Bold speaks with Sandra Bortek, representing the CRACoWi project, about the practical support CRACoWi can provide to SMEs and how Czech companies can benefit from the project’s activities.
Bringing CRACoWi closer to Czech SMEs
The interview introduces CRACoWi’s overall objective and the tools and resources being developed to make CRA compliance more manageable, particularly for SMEs, manufacturers, importers and distributors of products with digital elements.
One of the resources highlighted is the CRA Scope Check, already freely available through the CRACoWi website. The tool helps companies make an initial assessment of whether their product or service falls within the scope of the CRA. The interview also introduces the project’s CRAcademy, which provides webinars, workshops, FAQs, expert articles and other practical resources related to CRA implementation.
The discussion also covers the types of SMEs that can benefit from CRACoWi, the project’s ongoing use cases and pilots, and practical first steps for companies beginning their CRA compliance journey. Importantly, CRACoWi resources are available to SMEs across the EU, including companies based in the Czech Republic.
Extending CRACoWi’s reach through collaboration
Collaboration with organisations such as Frank Bold helps CRACoWi bring project knowledge and resources closer to companies in different European countries and connect with national SME communities.
We would like to thank Frank Bold and Kristína Šabová for the opportunity to introduce CRACoWi to their Czech audience and for supporting the dissemination of information about the tools and resources available to companies preparing for the CRA.
CRACoWi will continue developing and sharing practical resources through the CRAcademy and its other project activities to support companies in understanding and preparing for CRA requirements.
Understanding the Cyber Resilience Act (CRA) starts with understanding its language and that language isn’t always easy to navigate. Legal terminology, technical acronyms, and compliance concepts are scattered across the regulation and its supporting standards, often without a clear, accessible explanation in one place.
To close that gap, CRACoWi partners have developed the CRA Compliance Glossary, now available as a new resource on the CRAcademy hub. Built as part of CRAcademy’s mission to provide clear and practical information about the CRA (through FAQs, blogs, expert insights, and more) the glossary is designed to be your quick reference whenever CRA terminology gets in the way of getting things done.
The Glossary
The glossary brings together plain-language definitions of the terms, acronyms, and concepts that come up throughout the CRA compliance journey — from foundational security properties like confidentiality, integrity, and availability, to CRA-specific mechanisms such as the Declaration of Conformity, CE marking, and conformity assessment routes. It also covers the technical vocabulary manufacturers and product teams encounter in practice: SBOMs, SAST/DAST testing, threat modelling frameworks like STRIDE, vulnerability disclosure policies, and more.
Each entry is written to be understood without a legal or cybersecurity background, while staying precise enough to be useful for teams already deep in their compliance work.
The Cyber Resilience Act establishes uniform cybersecurity criteria for digital products placed on the EU market, covering the entire product lifecycle from design through decommissioning. For manufacturers, importers, and distributors (particularly SMEs without dedicated legal or cybersecurity teams) getting familiar with this vocabulary is often the first practical step toward compliance, well before documentation or technical measures come into play.
For those who prefer to save, print, or share the glossary offline, a PDF version of the CRA Compliance Glossary has also been published as an open-access download on Zenodo, ensuring the resource remains freely and permanently available to the wider CRA compliance community.
The glossary joins the CRAcademy webinar series and other capacity-building resources already available on the platform, reinforcing CRACoWi’s broader goal: helping SMEs, manufacturers, distributors, and importers meet new cybersecurity standards throughout the product lifecycle.
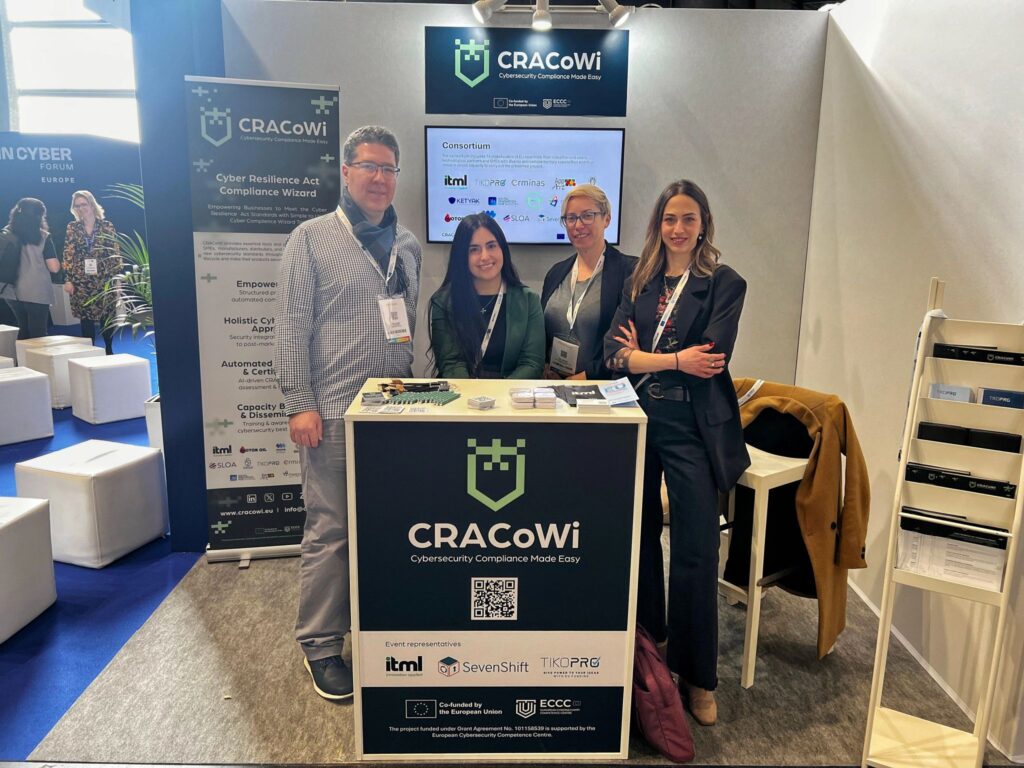
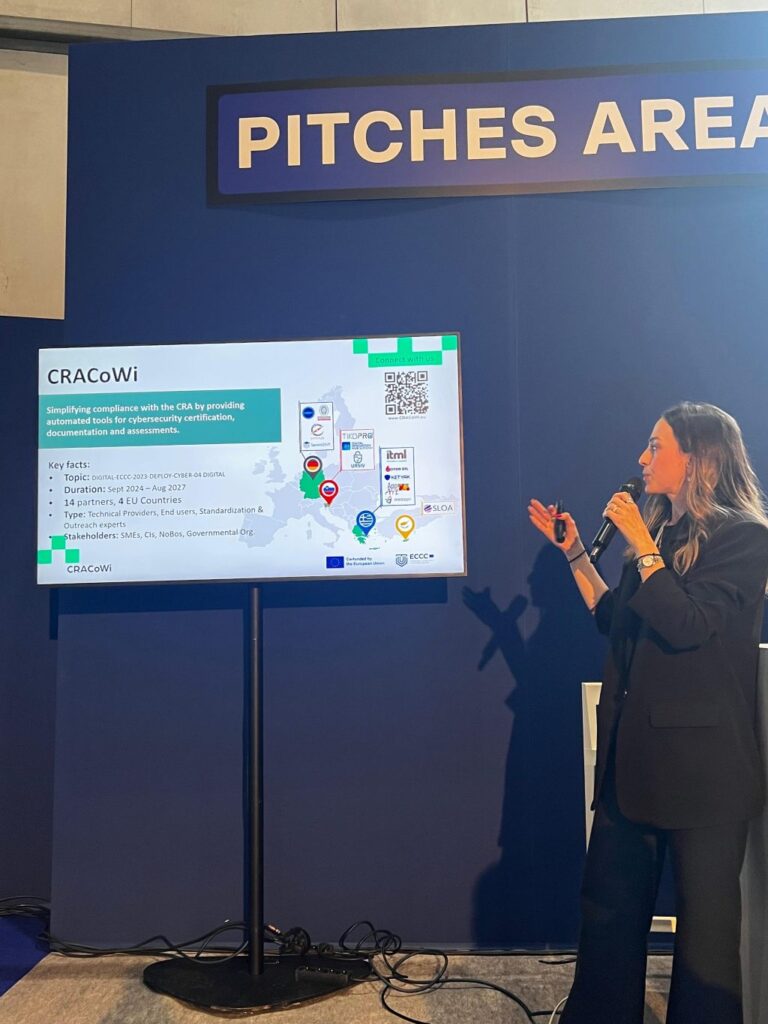
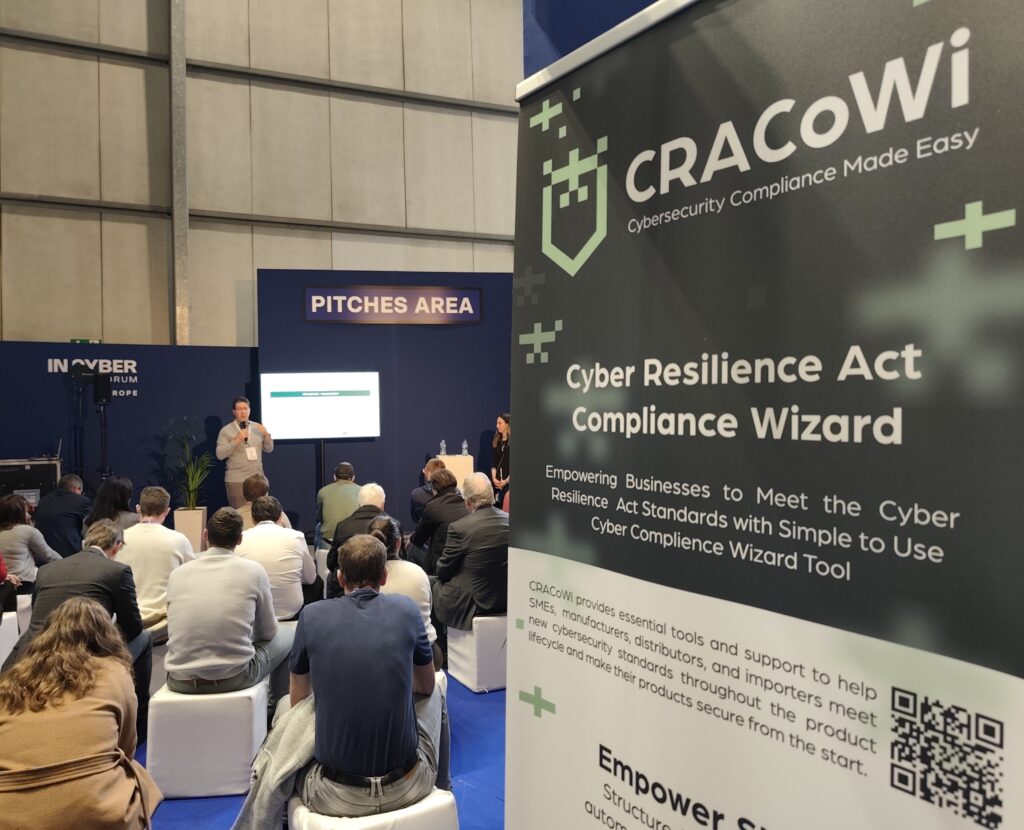
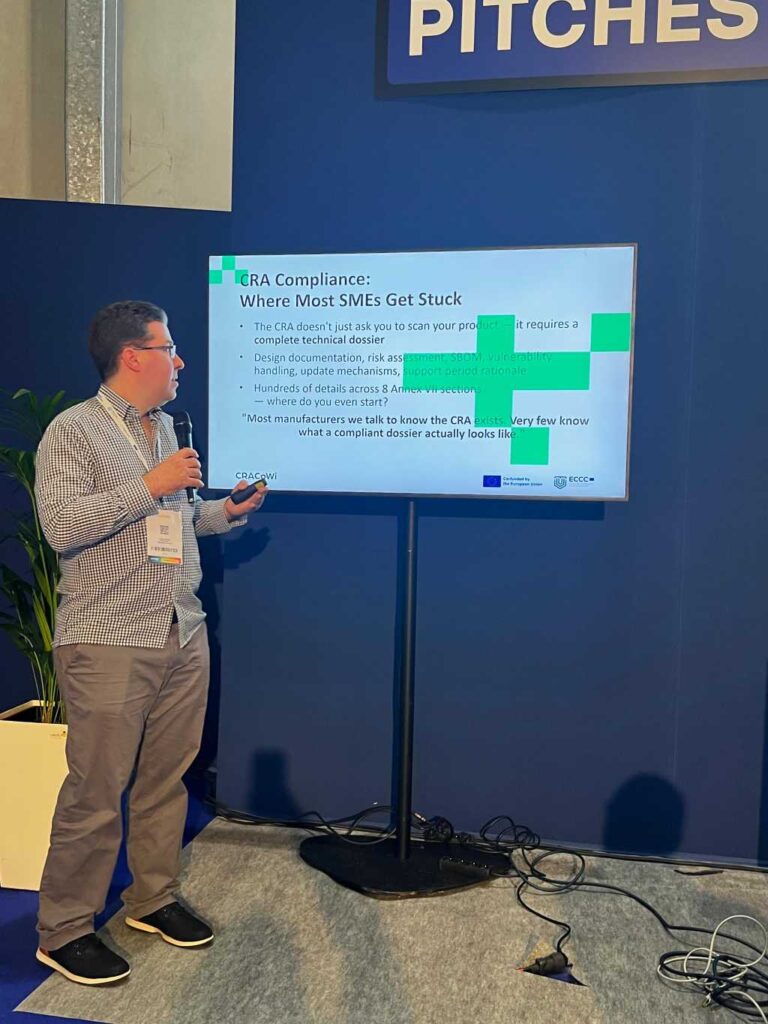
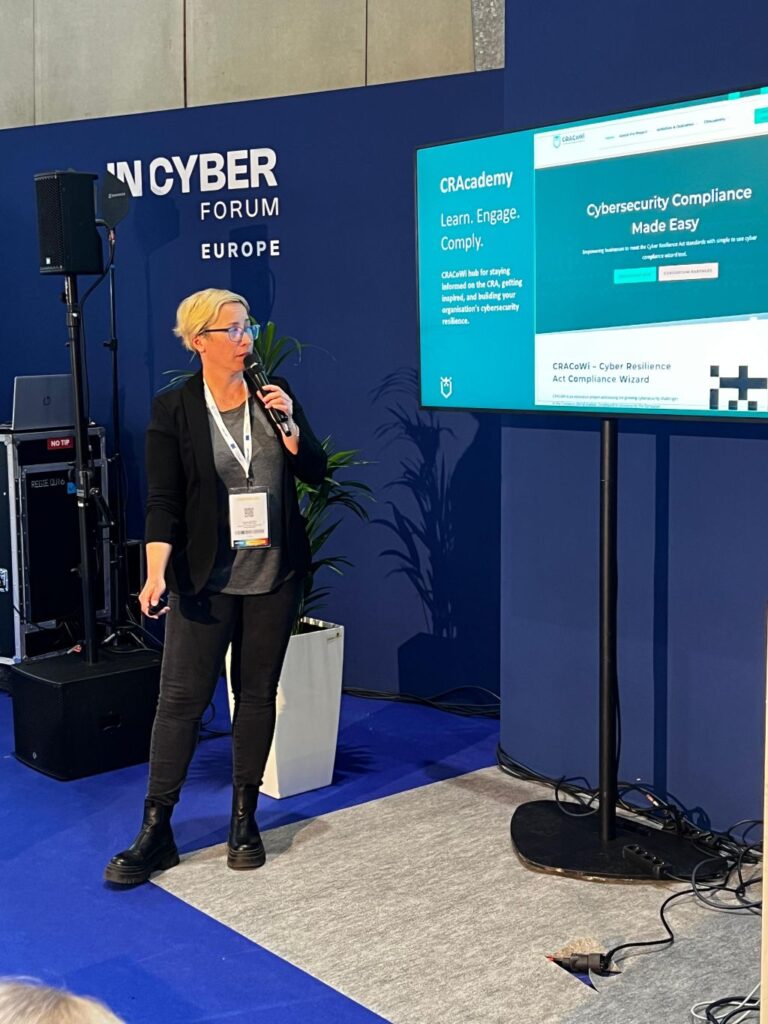
From 31 March to 2 April 2026, CRACoWi participated in the InCyber Forum Europe in Lille, France, one of Europe’s major events dedicated to cybersecurity and digital trust.
Represented by consortium partners ITML, SevenShift and Tiko Pro, CRACoWi joined the European cybersecurity community to present the project, exchange knowledge and explore opportunities for collaboration.
Throughout the three-day event, the project team engaged with companies and cybersecurity professionals, discussing the challenges organisations face when preparing for the Cyber Resilience Act (CRA) and the practical support they need to meet its requirements.
These exchanges provided valuable insights into real-world compliance challenges and stakeholder expectations, helping inform the ongoing development of the CRACoWi Wizard and its approach to supporting companies throughout their CRA compliance journey.
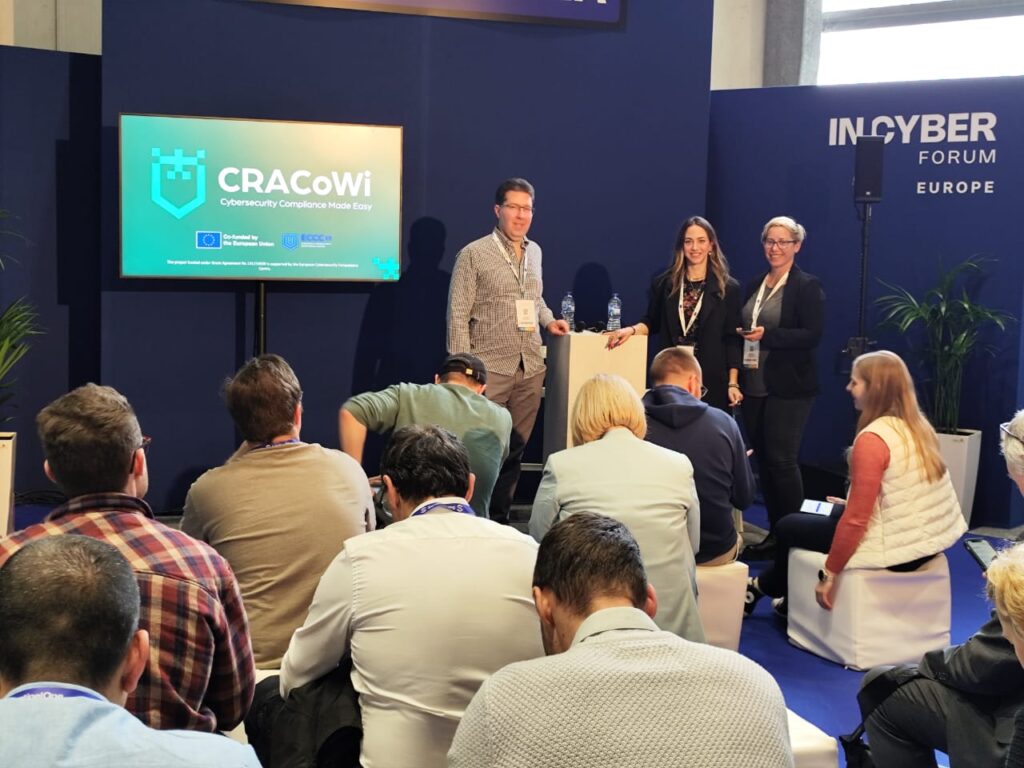
CRACoWi was also presented during dedicated sessions in European Pavilion delivered by Eleftheria Marini (ITML), Pablo Endres (SevenShift) and Sandra Bortek (Tiko Pro), introducing the project’s activities and practical approach to CRA compliance.
Participation in InCyber Forum contributed to CRACoWi’s communication, dissemination and stakeholder engagement activities, strengthening connections within the European cybersecurity ecosystem and opening opportunities for future cooperation.
We thank our participating partners and everyone who took the time to meet the CRACoWi team, share their experiences and discuss the challenges of cybersecurity compliance.
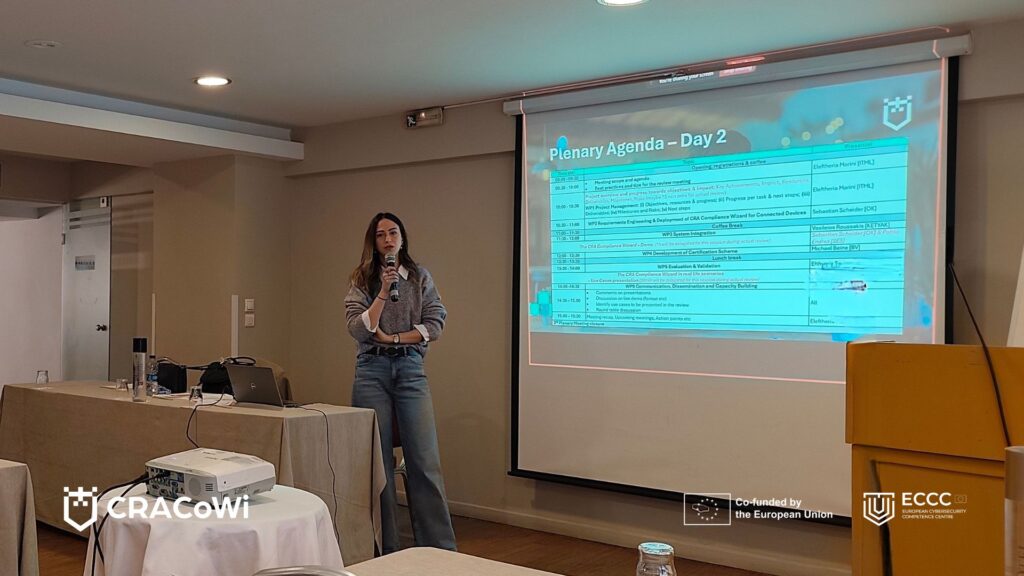
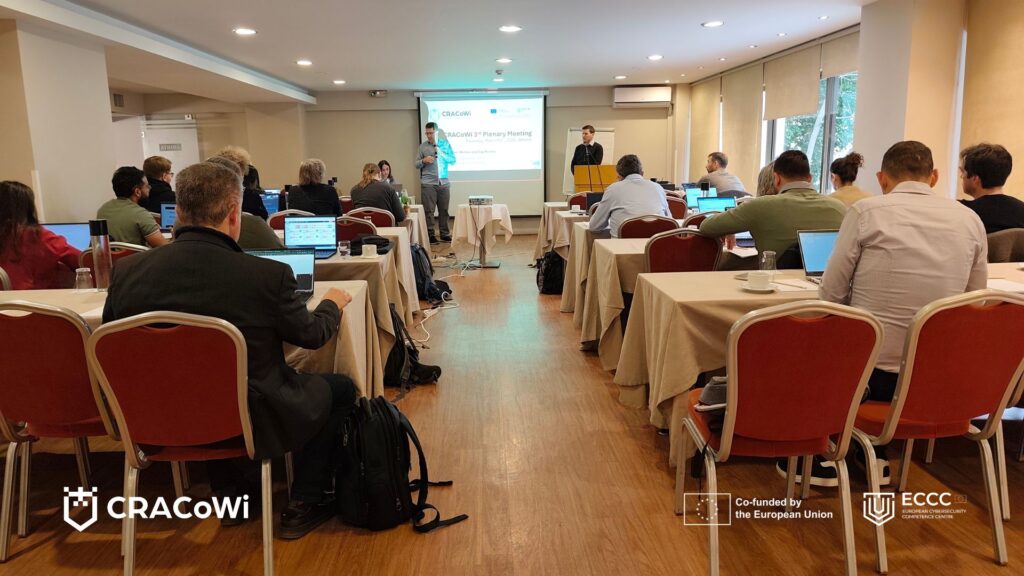
The CRACoWi consortium met in Athens last week for its latest plenary meeting, marking an important milestone as the project reached Month 18 of its implementation. The meeting focused on assessing progress, aligning next steps, and preparing for the upcoming midterm review.
Now halfway through its 36-month journey, CRACoWi continues to advance its core objective of supporting companies in meeting the requirements of the Cyber Resilience Act (CRA). As the regulation introduces mandatory cybersecurity obligations for products with digital elements, the project is developing a practical Compliance Wizard to help SMEs, manufacturers, distributors, and importers navigate these requirements in a structured and accessible way.
At this stage, the project has moved beyond initial setup and into tangible implementation. In parallel, partners are actively working on use cases covering critical infrastructure and market actors such as importers and distributors, ensuring that the tool reflects real-world compliance challenges.
Beyond technical development, CRACoWi has established a strong foundation for stakeholder engagement and capacity building. Through initiatives such as the CRAcademywebinar series and targeted communication activities, the project is already reaching its key audiences and building awareness around CRA requirements and practical compliance pathways.
The Athens meeting served as a key checkpoint, confirming that the project is progressing according to plan and is well-positioned for the midterm review. Partners aligned on the consolidation of results, upcoming deliverables, and the next phase of development, which will focus on further validation, stakeholder uptake, and scaling of the solution.
As Europe moves closer to the implementation of the Cyber Resilience Act, initiatives like CRACoWi are becoming increasingly important. The project plays a critical role in translating complex regulatory requirements into practical tools that businesses can actually use, reducing the compliance burden and supporting a more secure and resilient digital market.