Meet CRACoWi at CRA Standards Unlocked in Bonn

๐Ÿ“…7 October 2026 | 9:00 โ€“ 17:00 CEST | CITYHUB, Am Hauptbahnhof 6, Bonn| Hybrid | English & Germany | Free

The CRACoWi team is heading to Bonn!

On 7 October 2026, CRACoWi will join fellow European projects, cybersecurity experts, standardisation specialists and companies at CRA Standards Unlocked โ€“ EU Tour in Bonn, part of a European workshop series dedicated to helping organisations understand and prepare for the Cyber Resilience Act (CRA).

CRACoWi partners Bureau Veritas, SevenShift, ONEKEY and Erminas will be there, and we invite companies, SMEs and other stakeholders working on CRA compliance to join us and meet the team.

From CRA Requirements to Standards and Practical Compliance

As companies move from understanding the Cyber Resilience Act towards its practical implementation, questions around standards are becoming increasingly important.

Which standards will support CRA compliance? How are harmonised standards being developed? What will they mean for product development and conformity assessment? And what practical tools are already available to help companies prepare?

CRA Standards Unlocked will bring these discussions together in one place.

The programme will cover the CRA standardisation process and the roles of European and national standardisation organisations, followed by presentations on horizontal and product-specific standards currently under development.

Participants will also hear about CRA market surveillance, implementation from a manufacturerโ€™s perspective and how CRA compliance could influence the European digital single market and cybersecurity landscape.

Discover CRA Compliance Tools and Support

Understanding the standards is only one part of preparing for the CRA. Companies also need practical ways to translate regulatory requirements into their own processes and products.

Dedicated sessions at the event will therefore introduce compliance tools and funding opportunities being developed through Digital Europe Programme projects.

This is also where collaboration between projects working within the wider CRA ecosystem becomes particularly valuable. By bringing together different expertise, tools and approaches, CRA Cluster initiatives can help companies find the support that best responds to their specific compliance challenges.

CRACoWi is contributing to this effort by developing practical support for organisations navigating the CRA, including the CRACoWi Wizard, CRAcademy resources and the free CRA Scope Assessment.

Meet the CRACoWi Team in Bonn

For CRACoWi, events such as CRA Standards Unlocked are an important opportunity not only to share what we are developing, but also to meet companies directly, hear about their challenges and exchange knowledge with other projects working towards practical CRA implementation.

Representatives from Bureau Veritas, SevenShift, ONEKEY and OIXIO Erminas will represent CRACoWi in Bonn.

If you are preparing for the CRA, working with products with digital elements or simply want to understand how standards and practical compliance tools can support your organisation, come and meet the CRACoWi team.

๐Ÿ“… 7 October 2026 | 09:00โ€“17:00
๐Ÿ“ CITYHUB, Am Hauptbahnhof 6, 53111 Bonn, Germany
๐Ÿ’ป Hybrid event โ€“ onsite and online participation

Onsite participation is limited, so make sure to register in advance.

Join us in Bonn and be part of the conversation on turning CRA requirements and standards into practical compliance.
Join CRACoWi at Cyber Day 2026 in Ljubljana

๐Ÿ“…15 October 2026 | 9:00 โ€“ 15:00 CEST | Ljubljana.tech, BTC Ljubljana | English | Free

How can companies move from understanding cybersecurity requirements to actually implementing them?

On 15 October 2026, CRACoWi will join cybersecurity experts, companies and European initiatives at Cyber Day 2026 in Ljubljana, an event dedicated to turning cybersecurity requirements into practical action and strengthening the cyber resilience of European companies.

As a partner of the event, CRACoWi will contribute its expertise on the Cyber Resilience Act (CRA) and present some of the practical support being developed to help companies navigate the path towards compliance.

Cyber Day will take place from 09:00 to 15:00 at Ljubljana.tech, Trg mladih 9, Ljubljana.

From CRA Requirements to Practical Action

The Cyber Resilience Act introduces new cybersecurity requirements for products with digital elements, creating new responsibilities for companies across the product lifecycle. For many SMEs, the challenge is not only understanding these requirements but also knowing how to approach them in practice. This will be one of the key topics addressed at Cyber Day.

Michael Beine from Bureau Veritas, CRACoWi partner and cybersecurity and regulatory compliance expert, will present โ€œCRA Explained for SMEsโ€, looking at what the regulation means specifically for smaller companies.

This will be followed by a CRACoWi tools demonstration by Jacek Trossen from ONEKEY, giving participants an opportunity to learn more about the practical support being developed within the project.

The programme will continue by moving from compliance to action, including a panel discussion dedicated to the question โ€œHow can SMEs become cyber resilient?โ€

Meet the Wider Cybersecurity Ecosystem

Cyber Day is not only about understanding regulation. It is also an opportunity to discover the organisations, projects, tools and funding opportunities available to companies working to strengthen their cybersecurity.

The programme will bring together representatives of the CRA Cluster and several Digital Europe projects, including CyberSynchrony, ALiEnS-SOC and INTERCEPT.

Participants will also hear about the wider cybersecurity support ecosystem and EU funding opportunities for cyber resilience.

Alongside the conference programme, the Cybervillage will provide space to meet experts, European projects and support organisations directly, exchange experiences and explore opportunities for further cooperation.

Who Should Join?

Cyber Day is designed particularly for micro, small and medium-sized enterprises looking to strengthen their cyber resilience and better understand the regulatory requirements affecting their businesses.

The event will be especially relevant for companies preparing for the Cyber Resilience Act, organisations looking for practical cybersecurity support, and stakeholders interested in the European cybersecurity ecosystem, available tools and EU funding opportunities.

Whether you are already working on CRA compliance or are only beginning to understand what the new requirements mean for your organisation, Cyber Day provides an opportunity to ask questions, meet experts and discover the support already available.

Meet CRACoWi in Ljubljana

For CRACoWi, Cyber Day is also an opportunity to meet companies directly, better understand the challenges they face and present the practical support the project is developing for CRA implementation.

If the Cyber Resilience Act is on your agenda, come and meet the CRACoWi team in Ljubljana. Talk to our experts, learn more about the project and discover how CRACoWi can support your journey towards CRA compliance.

15 October 2026 | 09:00โ€“15:00
Ljubljana.tech, Trg mladih 9, Ljubljana

Participation is free of charge, but registration is required.

Join us at Cyber Day 2026 and be part of the conversation on turning cybersecurity requirements into practical action.

Meet Us at the CRA Standards Unlocked Event in Lisbon

๐Ÿ“…17 September 2026 | 9:00 โ€“ 17:00 CEST | Venue Auditรณrio da Sede Nacional da Ordem dos Engenheiros, Lisbon | Hybrid | English & Portuguese | Free
CRACoWi consortium partner SevenShift will be attending “CRA Standards Unlocked – EU Tour in Lisbon,” a hybrid workshop dedicated to helping SMEs understand, prepare for, and comply with the EU Cyber Resilience Act (CRA). This whole-day event is organised by the EU-funded projects CYBERSTAND.eu and STAN4CRA.eu, with the support of the Ordem dos Engenheiros.

The session brings together rapporteurs from the European Standardization Organizations (ETSI and CEN-CENELEC), who will present the latest drafts of harmonised CRA standards currently under development and gather feedback directly from attendees.

What you can expect

  • A clear breakdown of what the CRA requires and what it means in practice for SMEs
  • Direct insight into which standards matter and how they support compliance
  • Presentations from CRA standards rapporteurs on the state of ongoing standardisation work
  • An overview of compliance tools, practical guides, and funding opportunities available through CRA-related EU-funded projects
  • Practical guidance tailored to SMEs on how CRA requirements translate into product development and conformity assessment processes

Pablo Endres from SevenShift will represent CRACoWi at the event, sharing insights from the project’s work on the Compliance Wizard and present a Bunkai demo as part of the CRACOWi toolchain.

If you’re attending, we’d love the opportunity to connect – stop by and say hello.


CRAcademy UC Workshop: An SME’s Perspective on the CRA

CRACoWi is launching a new workshop series built directly around the project’s real-world use cases – grounding CRA compliance in the day-to-day experience of the organisations actually living it, rather than presenting the regulation in the abstract.

Cybersecurity affects us all โ€“ including small and medium-sized enterprises:

๐Ÿ“… 2 September 2026 โŒ›11:00-12:00 CEST ๐Ÿ“Online, free

This first session features Erminas, a software SME building solutions for industrial digitalisation and one of CRACoWi’s use case partners. Speaking from first-hand experience, Erminas shares what it actually takes to respond to a security incident without a dedicated security department and how the Cyber Resilience Act (CRA) can turn that experience from chaotic firefighting into a structured, manageable process.

Rather than a theoretical overview of the regulation, this online workshop walks through a realistic incident scenario step by step, showing how a few practical tools and habits (not a large security organisation) can meet the CRA’s core demand: traceability.

What you’ll learn:

  • Why SMEs carry the same cybersecurity responsibility as large enterprises, with far fewer resources
  • A real-world walkthrough of responding to a vulnerability: using an SBOM to scope affected products, checking patch status, applying a lightweight threat model, and communicating clearly with customers
  • Practical, low-overhead practices – Security Champions, regular awareness training, and frameworks like the NIST Cybersecurity Framework – for building traceability without building a full security department
  • Why structured processes reduce stress internally and build trust externally, especially in critical moments

Who should attend

Founders, engineering leads, and product teams at SMEs developing or maintaining software or connected products, especially those without a dedicated cybersecurity function and looking for realistic, teamwork-based ways to prepare for CRA compliance.

The presenter: Jonas Gerlach

Cybersecurity Team Lead & IIoT Developer with 8 years of hands-on experience designing, implementing, and securing industrial systems. Passionate about bridging operational technology (OT) and information technology (IT), leading technical teams, and delivering secure, scalable IIoT solutions.

Save the date and register!

๐Ÿ“… 2 September 2026 โŒ›11:00-12:00 CEST ๐Ÿ“Online, free

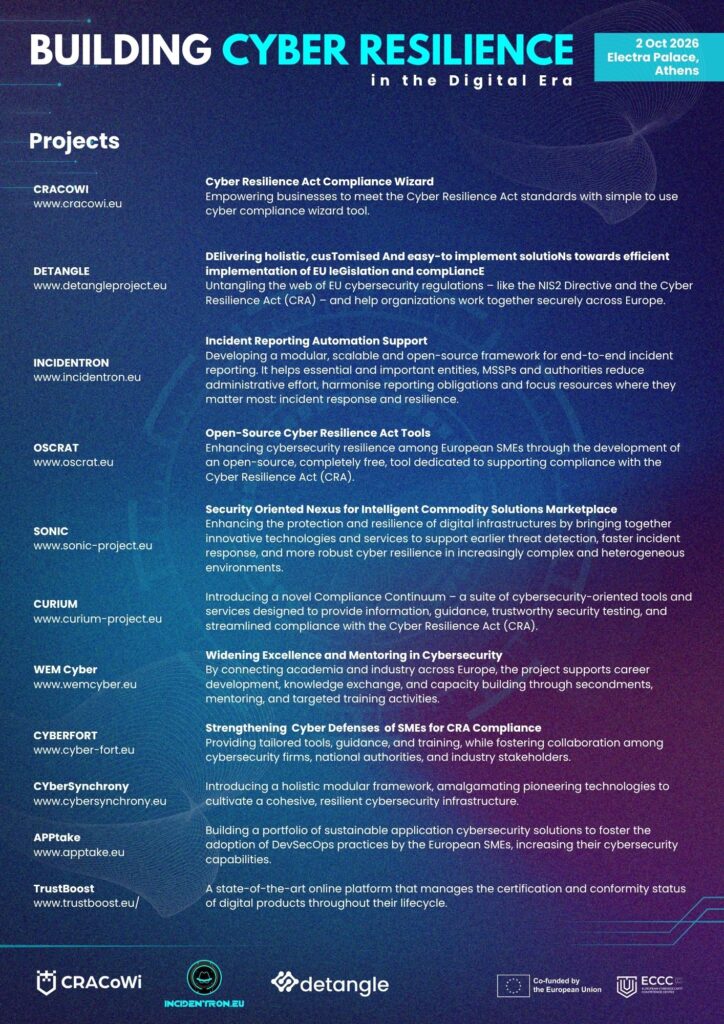
Event: Building Cyber Resilience in the Digital Era

A joint workshop on NIS2 compliance, CRA enforcement, and cross-border cybersecurity incident response.

๐Ÿ“… Friday, 2 October 2026 ๐Ÿ•˜ 09:00 โ€“ 16:00 ๐Ÿ“ Electra Palace Athens – 18-20 N. Nikodimou str, 10557 Athens, Greece ๐ŸŒ Language: English

The EU cybersecurity regulatory landscape is evolving fast – and organisations across every sector are being asked to keep pace. Building Cyber Resilience in the Digital Era is a high-impact workshop organised by the EU-funded projects CRACoWi, DETANGLE, and INCIDENTRON, bringing together policy, practice, and peer projects for a single day of focused, practical exchange.

The event centres on three interconnected themes shaping the future of digital resilience in Europe:

  • NIS2 compliance – what implementation really looks like in practice
  • Cyber Resilience Act (CRA) enforcement – what to expect as the regulation takes hold
  • Collaborative, cross-border cybersecurity incident response – how sectors and countries can work together more effectively when it matters most

This is not a theoretical policy briefing. It’s a working session designed to give attendees concrete tools, honest insights from the field, and direct access to the people building solutions to help organisations comply and stay resilient.

What You Will Gain

The workshop will provide practical guidance, real-world insights, and interactive discussions to help organisations strengthen resilience and meet evolving EU cybersecurity obligations. It moves beyond theory to deliver actionable guidance for organisations navigating the new EU cybersecurity regulatory landscape – whatever stage of the compliance journey they’re at.

What to Expect

Presentations from peer EU-funded projects See the tools and services being developed across Europe’s cybersecurity project landscape, and learn how relevant stakeholders can put them to use to strengthen readiness and achieve compliance.

Expert-led discussions A special focus on the practical challenges of NIS2 implementation, expectations around CRA enforcement, and strategies for effective cross-sector, cross-border collaboration in incident management.

Active participant engagement Ask questions, engage with experts and peers, and take part in an open survey and discussion to share your concerns, priorities, and interest in testing the projects’ solutions.

Networking lunch A valuable opportunity to continue the conversation and build lasting connections within the cybersecurity community.

Who Should Attend

This event is open to a broad audience, including:

  • SMEs, startups, and enterprises
  • Business leaders and decision-makers
  • Cybersecurity professionals
  • Legal and compliance experts

Regardless of sector, any organisation seeking to better understand and prepare for EU cybersecurity regulations will benefit from participating.

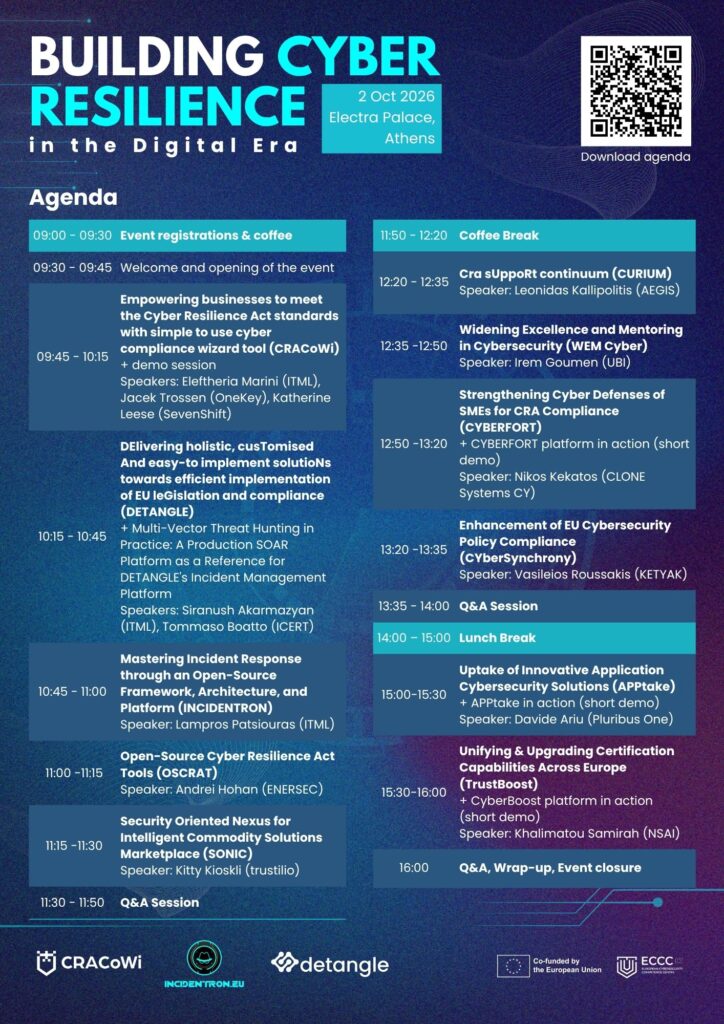
Agenda

Use the link below or the QR to download agenda.

Project that will join the event

Join Us

Whether you’re leading compliance efforts, shaping strategy, or working on the ground to strengthen your organisation’s cyber resilience, this is a chance to learn directly from the projects building Europe’s cybersecurity toolkit – and to help shape what comes next.

๐Ÿ“… Friday, 2 October 2026 ๐Ÿ•˜ 09:00 โ€“ 16:00 ๐Ÿ“ Electra Palace Athens – 18-20 N. Nikodimou str, 10557 Athens, Greece ๐ŸŒ Language: English

CRACoWI Partner erminas to Contribute to German Webinar on the Cyber Resilience Act on 19 June

The Cyber Resilience Act (CRA) is increasingly becoming a topic of discussion among companies across Europe. While organisations are working to understand the new requirements, many are asking a more fundamental question: how can they develop products that remain secure and trustworthy throughout their lifecycle?

To support this transition, CRACoWI consortium partner erminas GmbH will participate in the upcoming German-language webinar organised by IHK Oldenburg in cooperation with CYBERsicher โ€“ Transferstelle Cybersicherheit im Mittelstand.

๐Ÿ“… 19 June 2026, 10:00 – 12:00 AM CEST | online

During the webinar, Dr. Yvette Teiken (erminas GmbH) and Dr. Matthias Kampmann (EASY.CRA) will provide both a regulatory overview and practical perspectives on implementing the CRA.

Participants will gain insight into:

  • what the CRA regulates and who it affects;
  • why the European Union is introducing these requirements;
  • practical challenges related to Software Bills of Materials (SBOMs), vulnerability management, and documentation obligations;
  • pragmatic approaches for integrating CRA requirements into existing processes.

The session is aimed at SMEs with digital products, machinery and plant manufacturers, IoT manufacturers, and professionals working in IT, product development, and compliance who want to prepare for the CRA in a structured and practical way.

For CRACoWI, participation in events such as this reflects the project’s commitment to sharing knowledge beyond the consortium, engaging directly with industry stakeholders, and contributing to the broader European effort to help organisations navigate the transition towards CRA readiness.

๐Ÿ‘‰ Further information and registration are available via the IHK Oldenburg event page: MORE INFO & REGISTRATION

CRAcademy Webinar: How CRA Tools Simplify Compliance

Understanding the scope of the Cyber Resilience Act (CRA) is one thing; meeting its requirements in practice is another.

As the CRA prepares to replace the cybersecurity requirements under the Radio Equipment Directive from December 2027, manufacturers are entering a new phase of readiness. The challenge is no longer just understanding the regulation, but translating legal obligations into compliant products, practical processes, and demonstrable evidence.

To support organisations on this journey, the CRACoWi project invites you to join the next session of the CRAcademy webinar series From Pain Points to Market Readiness – How CRA Tools Simplify Compliance, on 25 June 2026, at 11 AM CEST.

This practical webinar focuses on the reality of CRA implementation. Drawing on experiences from the field, it explores the recurring issues that often delay manufacturers on their path to compliance and demonstrates how a new generation of CRA tools can transform slow, manual activities into structured and repeatable processes.

Participants will gain insight into some of the most common pain points organisations encounter, including incomplete interface inventories, cryptography gaps, and documentation that cannot be easily verified. The session will show how these challenges can be addressed in ways that are actionable for product teams and aligned with the expectations of the regulation.

Designed as a bridge between regulation and engineering reality, the webinar will help attendees better understand what practical CRA readiness looks like and how organisations can prepare efficiently for market placement and future certification activities.

This session is particularly relevant for:

  • Manufacturers of connected and digital products;
  • Engineers, system architects, and product security teams;
  • Product managers and compliance professionals translating requirements into implementation;
  • SMEs preparing for CRA implementation and certification.
    What will you learn?

By attending, you will:

  • Understand why security-by-design sits at the heart of the CRA;
  • See who is responsible for what across manufacturers, consultants, and notified bodies;
  • Recognise the common pain points that lead to costly delays and understand why they occur;
  • Learn how CRA tools reduce manual, error-prone work into repeatable processes;
  • Get direct answers to your questions during the live Q&A session.

๐Ÿ“… 26 June 2026 ๐Ÿ•š 11:00 AM CEST | ONLINE

Participation is free of charge.

๐Ÿ‘‰ Register today and take the next step from compliance pain points to market readiness.

Meet the Speaker

The session will be presented by Katherine Leese from SevenShift.

Originally from New Zealand and now based in Cologne, Germany, Katherine brings a unique and practical perspective to cybersecurity. After retraining in her forties to become an IT specialist for system integration, she combines hands-on technical experience with an understanding of the real-world challenges organisations face when implementing cybersecurity requirements.

As part of the CRACoWi project, SevenShift contributes to raising awareness about the Cyber Resilience Act and developing practical tools to support compliance. Katherine’s work focuses on helping bridge the gap between regulatory expectations and engineering reality, making complex requirements more understandable and actionable for manufacturers and SMEs alike.

Outside of work, she enjoys parenting a teenager and exploring how technology connects to everyday life.

If you are looking for practical guidance on moving from understanding the CRA to implementing it, this webinar is designed for you.

Participation is free of charge.

๐Ÿ‘‰ Register today and take the next step from compliance pain points to market readiness.

SevenShift Participating in Cybersecurity Competence Group Meeting in Cologne

On 12 May 2026, the CRACoWi consortium partner SevenShift participated in the meeting of the Cybersecurity Competence Group titled โ€œCyber Resilience in Practice: Strategies for a Secure Digital Futureโ€, held in Cologne, Germany.

The event gathered cybersecurity experts, industry representatives, and practitioners to discuss current challenges related to cyber resilience, the evolving threat landscape, and the practical implementation of the Cyber Resilience Act (CRA).

During the session โ€œThe Cyber Resilience Act: Legal Framework and Practical Experienceโ€, Katherine Leese from SevenShift (SES) contributed to the discussion by sharing practical experiences from CRA compliance testing and presenting CRA-related tools developed through EU-funded initiatives. As part of the presentation, Katherine introduced the CRACoWi Wizard, highlighting how the project supports organisations in understanding and implementing CRA requirements in practice. Complementary tools developed within other CRA Cluster projects were also presented, underlining the importance of collaboration and alignment between related initiatives.

The discussion addressed several important topics linked to CRA implementation, including reporting obligations and deadlines, responsibilities across the supply chain, security-by-design principles, lifecycle responsibility, and practical challenges organisations face when preparing for compliance.

The meeting also explored broader cybersecurity resilience topics beyond regulatory compliance itself. Discussions focused on the changing threat landscape, including stolen credentials, infostealer malware, residential proxy usage, and increasingly rapid attack execution following successful infiltration. Additional presentations addressed automated vulnerability management, CSAF, and security.txt as important mechanisms for more structured and scalable vulnerability communication.

Participation in events such as this supports CRACoWiโ€™s ongoing efforts to exchange practical knowledge, engage with cybersecurity communities, and strengthen cooperation with related initiatives working on CRA implementation and cyber resilience across Europe.

Katherine Leese (SevenShift)

CRACoWi at the Cluster Synergies Webinar

CRACoWi recently participated in the Cluster Synergies Webinar held on 22 April 2026, an event that brought together EU-funded cybersecurity projects to exchange insights, present ongoing work, and explore areas of alignment.

While such events are often framed as dissemination activities, their real value lies in something deeper – connecting initiatives that are addressing the same regulatory and technical challenges from different angles.

As the Cyber Resilience Act (CRA) moves closer to full implementation, the landscape of tools, methodologies, and support mechanisms across EU projects is rapidly expanding. Without active collaboration, this risks becoming fragmented. The Cluster Synergies Webinar is one of the spaces where this fragmentation can be addressed early – through open exchange, comparison of approaches, and identification of complementarities.

During the session, Pablo Endres (Seven Shift)and Sandra Bortek (Tiko Pro) presented the CRACoWi project, focusing on three key elements:

  • The development of tools supporting CRA compliance
  • The current progress and direction of the project
  • The CRAcademy, which provides structured training and practical guidance to help organisations better understand and implement CRA requirements

The discussion confirmed a recurring point across projects: organisations are not lacking awareness of the CRA – they are lacking clarity on how to act. This is where coordinated efforts between projects become essential. Each initiative contributes a different piece – whether technical tools, training, certification support, or implementation guidance – and together they form a more complete ecosystem.

Engaging with other EU initiatives also opens the door to joint dissemination, shared learning, and potential integration of approaches, ultimately increasing the impact of all projects involved.

The recording of the webinar is available here: